Praevanta
praevanta CYBERSECURITY, TECHNOLOGY, PREVENTION, ADVISED AS ONE
Cyber Strategist · Boardroom Advisor · Digital Trust Leader

Turning cyber risk into business resilience.

Praevanta advises boards, promoters and executive teams on cyber risk, sovereign AI and technology governance in regulated, high-consequence environments. Every engagement is led personally by our founder, drawing on twenty-four years of zero-failure operations across defence and a $60B+ industrial group.

Request a briefing Our practices
The record
RECORD
{{ v0 }}
Years in zero-failure environments
{{ v1 }}
Technology assets under custody
{{ v2 }}
Attack surface reduction delivered
{{ v3 }}
Operating companies secured
The Capability Set

Everything a board asks for, held in one engagement.

Twenty-four years · Zero-failure environments
24yrs
Operating record
Layered defence
Exposure
reduced
Breaches on watch
Threat
intelligence
Board-ready reporting
The most defensible posture a regulated enterprise can hold
Incident command
Layered shield representing the Praevanta operating picture
Readiness
Continuous assurance
Mapped to framework
Always-on monitoring
Rapid response
The Praevanta method
Forensic replay
Signal, not noise
Markets We Serve

Six interconnected industry ecosystems. The entire economy within reach.

01

Financial Services, Capital & Investment

Banking · NBFCs & lending · Payments & fintech · Insurance · Capital markets · Asset & wealth management · Private equity · Venture capital · Funds · Portfolio companies · Family offices

02

Energy, Infrastructure & Natural Resources

Power & utilities · Renewables · Oil & gas · Mining & metals · Water · Telecom · Data centres · Transport & logistics · Aviation · Maritime · Railways · Construction · Real estate

03

Government, Defence & Public Services

Central, state & local government · Defence & aerospace · Public sector undertakings · Law enforcement · Smart cities · Citizen services · Public administration

04

Manufacturing, Industrial & Mobility

Industrial manufacturing · Automotive · Engineering · Electronics · Semiconductors · Chemicals · Textiles · Food processing · Agriculture & agri-tech

05

Technology, Consumer, Media & Business Services

IT & ITES · SaaS · Cloud & AI · E-commerce · Retail · FMCG · Media & entertainment · Travel & hospitality · Professional services

06

Healthcare, Life Sciences, Education & Social Impact

Hospitals · Diagnostics · Pharmaceuticals · Biotechnology · Medical devices · Health-tech · Research · Education & edtech · NGOs · Foundations

Board-level cyber risk governance Zero ransom paid, full recovery in 24 hours Sovereign LLM platforms inside your perimeter 70% attack surface reduction OT / ICS / SCADA for critical infrastructure RBI · SEBI · DPDP · ISO 27001 · NIST CSF
Practices

Three practices, one accountable partner
All twenty services

Cyber Defence

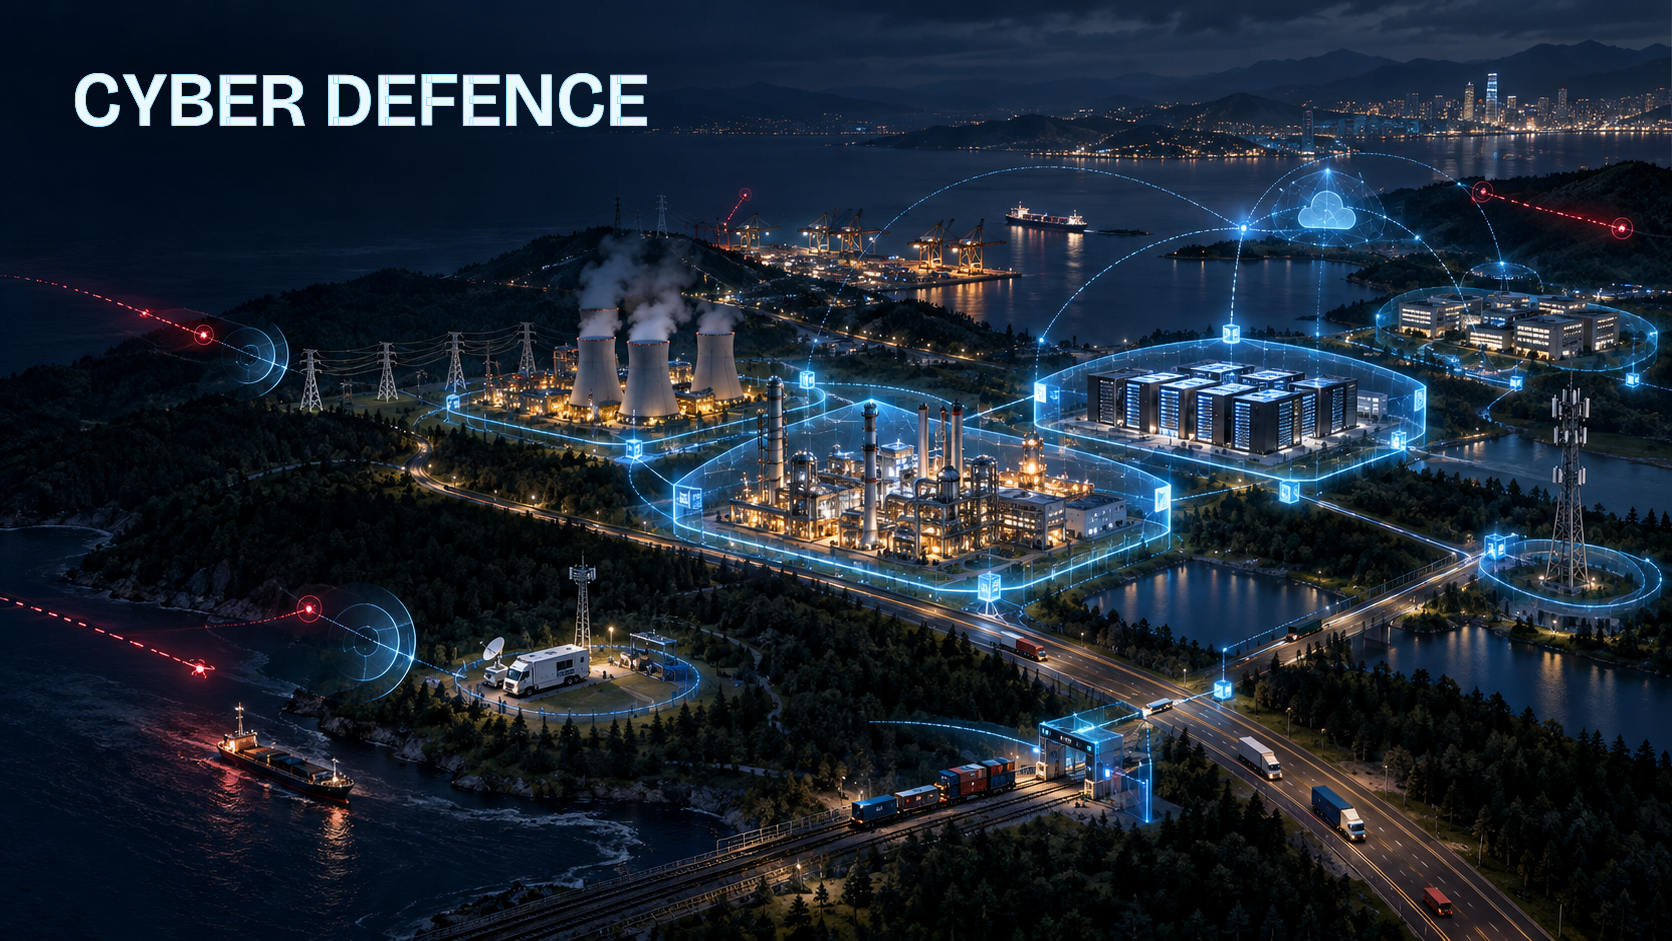
Architecture, detection and response for environments where downtime is measured in crores per day. Zero Trust design, OT and SCADA protection, cloud migration and security, DevSecOps, SOC build-out, threat hunting, supply chain and incident readiness.
9 services

AI & Data

Private models on your own infrastructure, and a transformation roadmap that survives audit. Sovereign LLM deployment, AI strategy, governance and compliance, maturity and posture, red teaming, data foundations.
6 services

Advisory & Governance

The seat at the table. Board and promoter advisory, fractional security leadership, regulatory readiness, technology due diligence for investors, executive briefings.

5 services
Where to start

Three doors, one accountable partner

Board Advisory
Boards & promoters

Board Advisory

A standing seat at the table on cyber risk, AI strategy and technology governance. Quarterly reporting the audit committee can actually read.

The firm →
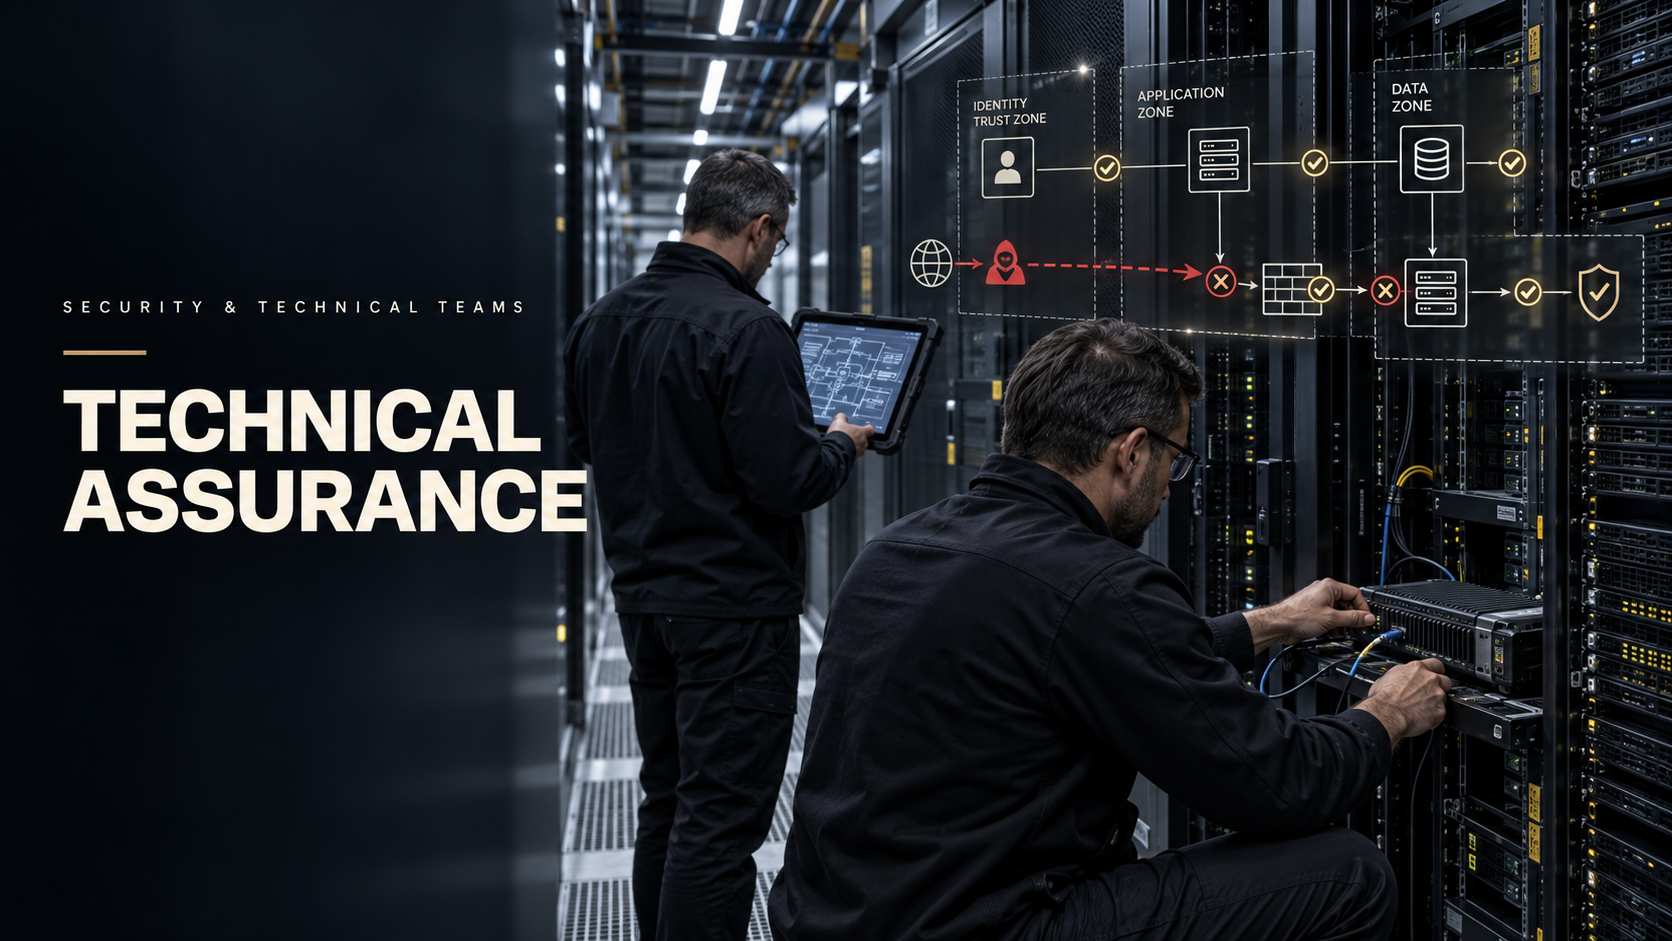
Technical Assurance
Security & technical teams

Technical Assurance

Architecture review, Zero Trust design, red teaming and control testing carried out to defence-grade standard, on your infrastructure.

Services →
Crisis & Response
Under active threat

Crisis & Response

Incident response, containment and recovery, run against protocols rehearsed long before the call comes in.

Enquire →
Method

Assess, architect, operate

Engagements run as retainers, defined projects, or an advisory board seat. Whichever the shape, the sequence holds.
I

Assess

Six weeks to an honest picture: threat exposure, control maturity, regulatory gaps, and what the board has not been told. Bad news first.
II

Architect

A sequenced plan with named owners, budget envelopes and board-reportable milestones. Designed against MITRE ATT&CK and the regulators you actually answer to.
III

Operate

We stay until your team can run it without us. Capability transfer is written into the engagement, not offered as an afterthought.

Selected work

Programmes our founder built and ran

All case studies
01
Sovereign AI

A private LLM platform, sealed inside the perimeter

An open-source foundation model fine-tuned entirely on the group’s own contracts, filings and workflows, then deployed on internal infrastructure. Legal, finance and tax teams use it daily. No data leaves the building.

Zero data egress
T+24H
02
Incident response

Multi-vector ransomware, no ransom paid

Pre-tested continuity protocols brought full enterprise operations back online within 24 hours. The plan worked because it had been rehearsed long before anyone needed it.

24 hrs to full operations
03
Critical infrastructure

A zero-day in energy billing, caught before the quarter closed

SCADA networks hardened for a distribution utility serving eight million customers, and a billing-system flaw found that had been costing roughly INR 1 crore a day.
INR 1 cr a day recovered
Founder

Led personally, every engagement

Praevanta was founded by PM Ramdas, a fifteen-year Indian Navy signals intelligence officer who went on to serve as Group Chief Technology Officer and Head of Cybersecurity for a $60B+ multinational conglomerate, reporting directly to the Chairman.

Boards do not buy methodology. They buy the judgement of the person in the room. He is in the room.

Full profile
Common questions

What people ask before engaging us

{{ item.num }}

{{ item.q }}

{{ item.sign }}

{{ item.a }}

The breach you defend in 2030 begins with the architecture you choose today.

Tell us what keeps the board awake. We will tell you plainly whether we can help.

Send an enquiry
Services

Twenty service lines, three practices

Engagements are shaped as a retainer, a defined project, or an advisory board seat. Scope is written to outcomes, not deliverable counts.

01

Cyber Defence

Zero Trust & security architecture

Identity-first architecture mapped to MITRE ATT&CK, with segmentation, XDR and SOAR automation designed for a real estate of legacy systems rather than a greenfield diagram.

OT / ICS & critical infrastructure

SCADA and plant-floor security for power, utilities and manufacturing, where a control system cannot simply be patched on a Tuesday afternoon.

Incident response & continuity readiness

Playbooks, tabletop exercises and recovery rehearsals. We test the plan while nothing is burning, so the plan holds when something is.

Data centre & cloud build-out

From blank floor plan to audited facility: power, HVAC, network fabric, SOC and NOC, redundancy and sovereignty requirements specified layer by layer.

Threat intelligence & hunting

Intelligence scoped to your sector and adversaries rather than a generic feed, with proactive hunts across the estate for the activity a rule set was never written to catch.

Application security & DevSecOps

Security moved into the build: threat modelling at design, testing inside the pipeline, secrets and dependencies under control, so releases ship weekly without shipping exposure with them.

Cloud migration & deployment

Landing zones, tenancy design and workload migration across AWS, Azure and GCP, sequenced so the estate moves without a compliance gap opening mid-programme.

Cloud security & posture management

Identity, network and workload controls for multi-cloud and hybrid estates, with continuous posture management that catches the misconfiguration before the scanner on the internet does.

Third-party & supply chain security

Vendor, partner and contractor exposure mapped and tiered, with contractual controls and monitoring for the connections that sit outside your perimeter but inside your risk.

02

AI & Data

Sovereign AI & private LLM deployment

Open-weight models fine-tuned on your own corpus and hosted inside your perimeter, with the governance, logging and access control an auditor will ask for.

AI transformation strategy

Where machine learning earns its budget and where it does not. Use-case selection, build-versus-buy, shadow AI containment, and efficiency targets the board can hold you to.

AI governance, risk & compliance

Policy, model inventory, approval gates and audit evidence for the AI already running in your business, aligned to the EU AI Act, DPDP and sector regulators before an examiner asks.

AI maturity & security posture assessment

A graded read of where the organisation stands: AI capability by function, data readiness, and the security posture underneath both, scored against peers with a costed path to the next level.

AI red teaming & model assurance

Adversarial testing of the models you have shipped: prompt injection, jailbreaks, data leakage through inference, and the guardrails that hold once a determined user starts probing.

Data foundations & classification

Knowing what data you hold, where it sits and who can reach it, before any model is pointed at it. Classification, lineage, residency and retention built to survive both an audit and a breach.

03

Advisory & Governance

Board & promoter cyber-risk advisory

Risk translated into the language of capital and liability, with quarterly reporting a board can act on. Bad news first, softened for nobody.

vCISO & fractional security leadership

Senior security leadership on a defined cadence for organisations that need the judgement of a group CISO without the headcount, including hiring and mentoring the permanent successor.

Regulatory compliance & audit readiness

RBI, SEBI, DPDP, ISO 27001 and NIST CSF programmes built once and reused across entities, with evidence gathered as a by-product of operations.

Technology due diligence for investors

Pre- and post-deal assessment of a target’s technology estate, security debt and regulatory exposure, written for an investment committee rather than an engineering team.

Executive briefings & keynotes

Closed-door board sessions, leadership offsites and conference keynotes on cyber risk, sovereign AI and command under pressure.

Not listed here?

Post-quantum readiness, TSCM-swept executive communications and reputation defence sit outside the standard lines. Ask.

Start a conversation
Industries

Sectors where failure is not an acceptable outcome

Praevanta works with organisations whose downtime has a regulator, a headline, or a public consequence attached to it.

Banking, financial services & insurance

RBI and SEBI expectations, third-party risk across fintech partners, and fraud-adjacent controls that survive an inspection.

Power & utilities

Generation, transmission and distribution networks where OT and IT have quietly merged and nobody documented when.

Telecom & digital infrastructure

Carrier-scale networks, data centre estates and the sovereignty questions that follow customer data across borders.

Government & defence

National security networks, incident response doctrine and secure communications, informed by fifteen years inside the Indian Navy.

Manufacturing & heavy industry

Plant-floor continuity, supply chain exposure and the security case for connected operations that finance will actually approve.

Private capital & portfolio companies

Diligence before the cheque, and a hundred-day security plan for the portfolio company after it.

Healthcare & life sciences

Hospital networks, connected medical devices and clinical trial data, where an outage is a patient safety event and patient records are the most saleable data a criminal can hold.

Ports, shipping & logistics

Terminal operating systems, vessel and fleet networks and the customs interfaces between them, secured with the operational understanding that comes from fifteen years at sea.

Where we work

Headquartered in India, engaged globally

India GCC & Middle East APAC UK & Europe United States
The firm

Praevanta exists because most security advice arrives too late to matter

Our work sits upstream of the incident, the audit finding and the board escalation.

The name

PRAEVANTA is a coined name built around one central idea: creating advantage through foresight.

ΠΡΑΙΒΑΝΤΑ | برايفانتا | प्रैवांटा | പ്രൈവന്റാ | ПРАЙВАНТА | プライヴァンタ | 프라이반타 | 普莱万塔 |
PRAE

Latin prae, before, ahead or in advance.

VANTA

From vantage, tracing back to the Latin ante, in front, before.

Prae is Latin outright (prae, before). Vanta is not, it comes to us through vantage and advantage, both descended from the Latin ante (in front of, before) by way of Old French. Put next to each other, the two roots say the same thing twice: get there first.

Together, PRAEVANTA means the advantage of seeing risk before it becomes impact.

The brand story is simple. Most cybersecurity firms enter when a problem has already appeared. PRAEVANTA helps leaders see earlier, decide intelligently and act before threats, technology shifts or governance gaps become business crises.

Brand promise
See Ahead. Secure What Matters.
Short form
Ahead of Risk.
Praevanta advisory office overlooking a working port

We are a senior-only advisory practice. There is no pyramid of junior analysts learning on your estate, and no methodology deck standing in for judgement. Engagements are led personally by our founder and staffed, where scale demands it, with specialists he has worked alongside for years.

That model sets a deliberate ceiling on how many clients we hold at once. It also means the person who sits in your board meeting is the person who has run the programme before, in an environment where a missed signal was an incident rather than a bug ticket.

We take a position on independence. Praevanta does not resell technology and takes no vendor commissions. When we recommend a platform it is because it fits your estate, and you are free to buy it from anyone.

Operating principles

How we actually run things

Eight habits, threaded through every engagement in the same order.

01

Mission before org chart

Protect the operation first, then work out who reports to whom. Reorganisations can wait; exposure cannot.

02

Chart the water you have

Plans are written against the estate that exists, not the architecture diagram someone drew in 2019. We survey before we recommend.

03

Zero-failure discipline

Controls are tested against a hostile reader, not a compliance checklist. A 70% reduction in attack surface does not happen by accident.

04

Bad news first

Softening a vulnerability to keep a meeting comfortable is not diplomacy. It is a liability transferred to the board.

05

Calm command in a crisis

Response quality is decided in the rehearsals, months before the incident. We rehearse.

06

Log it for the next watch

Every decision, exception and residual risk is written down while it is fresh. The watch changes; the record has to survive the handover.

07

Build it so it does not need us

Capability transfer is a term of the engagement. A practice that makes itself permanent has confused revenue with results.

08

Sovereignty over convenience

If the easy option means your legal and finance data leaves the building, it is not actually the easy option.

Founder & Principal

PM Ramdas

Group CTO & CISO, Indian Navy veteran

Twenty-four years directing enterprise cybersecurity, AI-driven transformation and board-level risk governance, most recently as Group Chief Technology Officer and Head of Cybersecurity for a $60B+ conglomerate spanning banking, power, telecom, critical infrastructure and defence.

Before the boardroom, fifteen years as a signals intelligence officer in the Indian Navy, commanding more than a hundred personnel and helping found the Navy’s computer incident response team.

He writes at Bytes & Beyond and keeps the full career record at pmramdas.com.

$80M+
Annual budget deployed
$800M+
Revenue growth enabled
60%
Faster incident response
100+
Personnel commanded, Indian Navy
Certifications
Certified Ethical Hacker, EC-Council
Computer Hacking Forensic Investigator
EC-Council Certified Security Analyst
Licensed Penetration Tester
ISO 27001 ISMS Lead Auditor
Certified Information Systems Professional
Recognition
Best AI Leader, World AI Show, 2024
Best CIO, Enterprise Excellence, Economic Times, 2025
Top 100 Cybersecurity Leaders, IDC, 2024
Best CXO Security Leader, CXOTV, 2024
CSO100 The Resilient 100, IDC / Foundry, 2024
Education
DBA (pursuing), Quantum x AI x Cybersecurity convergence, Birchwood University
M.Sc, Cybersecurity & Cyber Laws, IMT Ghaziabad & NLU Jodhpur
Advanced Network Security Programme, IIT Kharagpur
B.Sc, Information Technology, Annamalai University
Track record

Twenty-four years where failure was not an option

Defence, then a $60B+ industrial group. The numbers below are what that record looks like in practice.

The record, twenty-four years
{{ v0 }}
years in zero-failure defence & industrial ops
{{ v1 }}
technology assets brought under custody
{{ v2 }}
average attack surface reduction delivered
{{ v3 }}
operating companies secured to date
$80M+
Annual budget deployed
$800M+
Revenue growth enabled
60%
Faster incident response
100+
Personnel commanded, Indian Navy
The story so far
01 · The problem

Most boards hear about a breach after it’s already cost them the quarter

02 · The standard

Twenty-four years spent where failure wasn’t an option: defence, then a $60B+ industrial group

03 · The firm

Praevanta exists so that standard doesn’t stay locked inside one organization

Case studies

Programmes our founder built and ran

A selection of the work behind the record. Full detail is shared under NDA during an initial conversation.

Sovereign AI

A private LLM platform, sealed inside the perimeter

An open-source foundation model fine-tuned entirely on the group’s own contracts, filings and workflows, then deployed on internal infrastructure. Legal, finance and tax teams use it daily. No data leaves the building.

Incident response

Multi-vector ransomware, no ransom paid

Pre-tested continuity protocols brought full enterprise operations back online within 24 hours. The plan worked because it had been rehearsed long before anyone needed it.

Critical infrastructure

A zero-day in energy billing, caught before the quarter closed

SCADA networks hardened for a distribution utility serving eight million customers, and a billing-system flaw found that had been costing roughly INR 1 crore a day.

Zero Trust

Group-wide Zero Trust across thirty operating companies

A framework mapped to MITRE ATT&CK with XDR and SOAR automation and a 24x7 global SOC, cutting attack exposure by 70% across fifteen business verticals.

Board & regulatory

A cyber risk register the board could actually read

Technical exposure translated into financial terms for the audit committee, with quarterly reporting against SEBI, RBI and DPDP obligations. Two regulatory inspections closed with no adverse findings.

Supply chain

Four thousand vendors, ranked by the harm they could do

A third-party assurance programme built from scratch: tiered diligence, contractual security clauses and continuous monitoring of the vendors with privileged access. Onboarding time fell by half.

Client word

In their words

Client references are shared directly on request, out of respect for the confidentiality most engagements require.

Client quote to be supplied.

Chair, listed group

Client quote to be supplied.

Managing Director, private bank

Client quote to be supplied.

Partner, growth fund
Speaking & media

Closed-door briefings and public keynotes

On cyber risk, sovereign AI and command under pressure, drawn from fifteen years in the Indian Navy and a decade at the top of enterprise security.

Board-level cyber risk

Translating technical exposure into the language of capital and liability, for the audience that signs off the budget.

Sovereign AI & digital trust

What it takes to deploy AI inside your own perimeter, and why trust is the architecture that makes the rest of it possible.

Command under pressure

Leadership lessons from bridge to boardroom: how fifteen years at sea shape decisions made in a crisis.

Booking for a board session, offsite or conference

Enquire about a booking
Insights

Thinking, published in the open

Our founder writes at Bytes & Beyond on cybersecurity, AI and what two decades of running security programmes teaches. Latest posts below.

Bytes & Beyond

Weekly dispatches on cyber, AI and command experience.

Read the blog
Enquiries

Tell us what keeps the board awake

Every enquiry is read by our founder. If Praevanta is not the right fit, we will say so and point you somewhere better.

Coverage
India, GCC, APAC, Europe and the US
Response
Within two working days

Anything you share is treated as confidential. We sign an NDA before the first substantive conversation if you prefer.

Received

Thank you. Your enquiry is with us.

You will hear back within two working days. If this is a live incident, write directly to hello@praevanta.com with INCIDENT in the subject line.